Security Within Our Platform Architecture
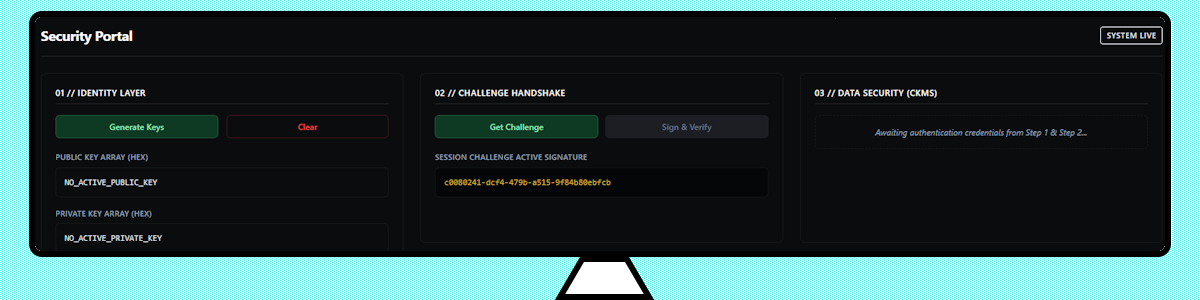
Current Security Portal (Screenshot)
Secure Thinking
We have put a lot of time into thinking about how to give customers sensible security when running our software.
Why? Quite simply - we use our software and want to give other customers the same solution.
This page will not reveal our precise approaches, but show the thinking behind our software.
Behaviour is Everything
What you do, how you interact, what you use, is the biggest security challenge
Once we delegate that to automation, we are abstracting away our control
Ultimately, manual intervention, maintaining risk is the ultimate control
You can block all access to your instance through the trading Exchange's API
Off-Exchange vs On-Exchange
We cannot advise on this, but our opinion is that cryptocurrency is a decentralised asset.
We prefer to consider a balance between off-exchange storage and on-exchange storage.
Customers must determine their own risk tolerance.
Risk Evaluations during Onboarding
We can tell you what we do and the attack vectors
We cannot provide full risk-free exchange automation through our software - few can!
Core Cryptographic Goals
Zero Knowledge Protocol
We have zero visibility into your private exchange credentials
Ephemeral Key State
No secure exchange keys exist on disk or inside any local database tables
Exchange Controlled Permissioning
You provision and scope your own API access permissions directly within your Coinbase dashboard
Immediate Access Revocation
You retain the absolute right to cancel your API provisioning directly inside the exchange immediately
Private Credential Control
You determine how to securely manage and store your master API secrets outside our runtime environment
Zero Access Auditing
We never log or audit your underlying private exchange connection keys
Complete Environment Sovereignty
You retain absolute structural control over the entire execution perimeter
Conclusion on Automated Exchange Security
Customers deserve to know how seriously we take security.
If you use open source software, please consider security in terms of how this software is provisioned.
We can help you with your own solutions, our software is modular and we may be able to help.